DEVELOPERS / WORKFLOWS / UPDATED 16 NOV 2026
Trigger a Label Workflow From Your Code
Start a LabelInn workflow from Python, Node.js or a shell: test with a sample row, mint a signed trigger, fire it with a record. Signature checked.
SECRET="whsec_..."                       # shown once, when the trigger was created
BODY='{"order_id":"ORD-9876","sku":"A-1042"}'
SIG=$(printf '%s' "$BODY" | openssl dgst -sha256 -hmac "$SECRET" | sed 's/^.* //')

curl -X POST https://labelinn.com/v1/workflows/wf_orders/trigger/TOKEN \
  -H "Content-Type: application/json" \
  -H "X-LabelInn-Signature: sha256=$SIG" \
  -d "$BODY"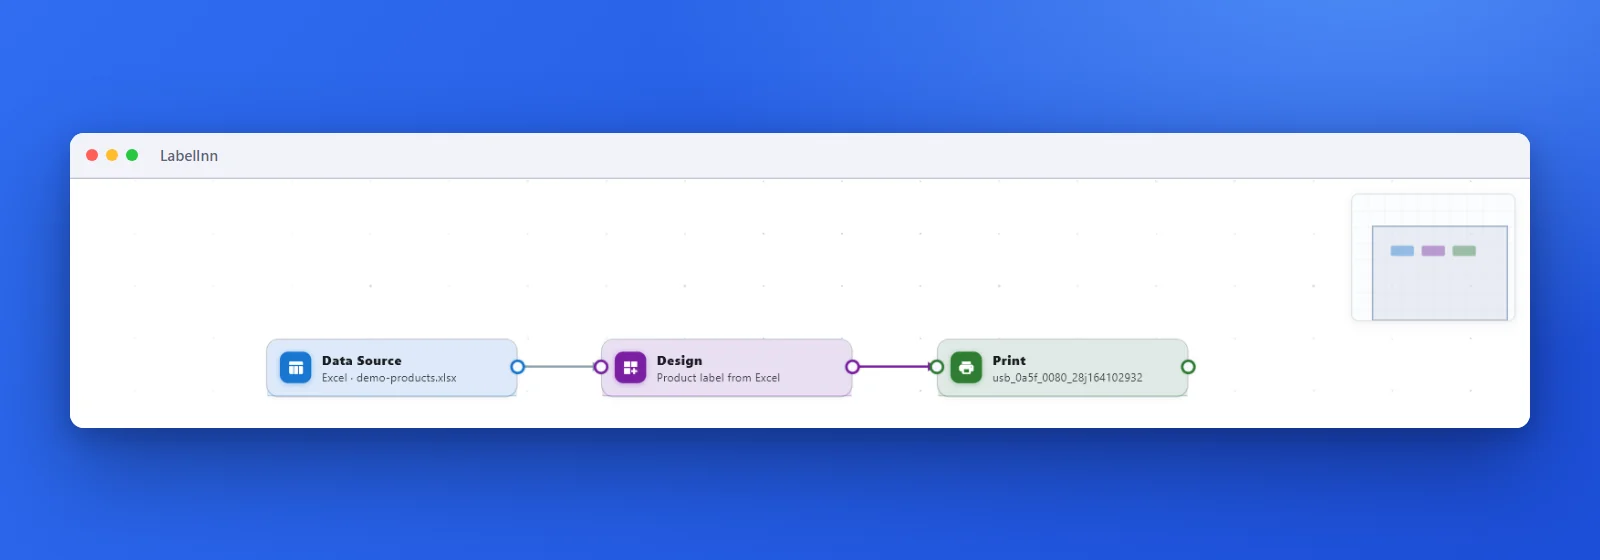
SHORT ANSWER
Build the printing logic as a workflow; your code starts it with one record.
Mint an inbound trigger once, then POST a JSON record to it from an ERP, a script or a webhook. The record becomes the workflow’s row, so every field is available to the design and the rules. A signed trigger refuses any request whose HMAC-SHA256 signature does not match the body.
workflows.testis a dry run: nothing prints.workflows.fireis a real run: labels print.- The token is the credential, so the trigger needs no API key.
01 / WHY
Why a workflow, not more code
Printing is rarely one call.
Pick the right design for the product, look up the missing fields, print one label per line, mark the order as printed, alert someone if it fails. Written in your application, every rule change is a code change.
In LabelInn you build that logic as a workflow, visually, and your code starts it with a record. The workflow can:
- Pick the design by product, customer or country.
- Look up missing fields in a file or database.
- Print one label per line, numbered "3 / 12".
- Write back that it printed.
- Alert someone when the printer needs attention.
02 / TEST
1. Test the workflow with a sample record
A test run walks the graph and prints nothing.
from labelinn import LabelInn

client = LabelInn("sk_live_...")

# 1. Dry run with a sample record: nothing prints
result = client.workflows.test("wf_orders", row={"order_id": "ORD-9876", "sku": "A-1042"})

# 2. Mint a signed trigger, once. Store token and secret now: the secret is shown once.
trigger = client.workflows.create_trigger("wf_orders", signed=True)

# 3. Fire it from your system. The SDK signs the exact request bytes with HMAC-SHA256.
run = client.workflows.fire(
    "wf_orders",
    trigger["token"],
    {"order_id": "ORD-9876", "sku": "A-1042"},
    secret=trigger["secret"],
)
The three steps in one file: test is a dry run (POST /v1/workflows/{id}/test); create_trigger mints an inbound trigger, and with signed=True a secret that is shown once; fire runs the workflow with your record. A fired run is real: labels print.
POST /v1/workflows/wf_orders/test
{"row": {"order_id": "ORD-9876", "sku": "A-1042"}}

POST /v1/workflows/wf_orders/triggers
{"signed": true}

POST /v1/workflows/wf_orders/trigger/tok_demo
X-LabelInn-Signature: sha256=37e59fb4...
{"order_id":"ORD-9876","sku":"A-1042"}
The token in the URL is the credential, which is what makes it safe to paste into an ERP button or a scanner macro. Revoke it with DELETE /v1/workflows/{id}/triggers/{token}. A signed trigger also refuses any request whose signature does not match the body.
03 / SIGN
2. Sign the request: SDK or a plain shell
No SDK needed: any HTTP client that can compute an HMAC works.
With a secret, the SDK signs the exact request bytes with HMAC-SHA256 and sends them as X-LabelInn-Signature: sha256=<hex>. From a shell, openssl does the same. The two produced the same signature for the same body, and an independent HMAC of the logged body matched it.
SECRET="whsec_..."                       # shown once, when the trigger was created
BODY='{"order_id":"ORD-9876","sku":"A-1042"}'
SIG=$(printf '%s' "$BODY" | openssl dgst -sha256 -hmac "$SECRET" | sed 's/^.* //')

curl -X POST https://labelinn.com/v1/workflows/wf_orders/trigger/TOKEN \
  -H "Content-Type: application/json" \
  -H "X-LabelInn-Signature: sha256=$SIG" \
-d "$BODY"body {"order_id":"ORD-9876","sku":"A-1042"}
Python SDK sha256=37e59fb47b1d2621...
openssl sha256=37e59fb47b1d2621...
independent HMAC of the logged body: matchconst LabelInn = require("labelinn");
const client = new LabelInn("sk_live_...");
(async () => {
const trigger = await client.workflows.createTrigger("wf_orders", { signed: true });
// Store trigger.token and trigger.secret now: the secret is shown once.
const run = await client.workflows.fire("wf_orders", trigger.token,
{ order_id: "ORD-9876", sku: "A-1042" }, { secret: trigger.secret });
console.log(run);
})();04 / PIECES
Where each piece lives
Your system on the left, LabelInn on the right.
| You want to | Use |
|---|---|
| Start a workflow from your code with a record | This page: fire on a signed inbound trigger |
| Print one design with your values, no logic | Print labels from code |
| Start a workflow from any HTTP client or webhook | Trigger printing from any API or webhook |
| Call from your language with run code and traps | Python, Node.js, C#, Go |
The workflow methods need SDK 3.0 or later: pip install -U labelinn, npm install labelinn@3, dotnet add package LabelInn --version 3.0.0, go get github.com/labelinn/labelinn-go/v3.
05 / TESTED
What was run for this page
Read this before you trust a snippet.
| Item | Run here? | Result |
|---|---|---|
| test, create_trigger, fire (Python and Node.js SDK) | Run with labelinn 3.1.0 (PyPI, npm) | Against a local stand-in. The requests and the signature are real SDK output; the stand-in’s answers to these three routes are not shown because they are not a captured response of the live service. |
| Signature | Run | SDK, openssl and an independent HMAC agree on the same body. |
| C# and Go workflow calls | From the SDK sources | Not run here; see the language pages. |
| The live service, a physical printer | Not used | No request went to labelinn.com and nothing was printed. |
06 / PLANS
What is free and what needs a plan
Workflows start on Starter; the production API is Pro.
FREE
$0
- Design and print by hand, with no label limit
- API sandbox:
sk_test_key, read-only, 25 calls a day - Workflows and automations are not in Free
STARTER
$7.99 / month
- Everything in Free
- Workflows and automations
- API sandbox: 250 calls a day (read-only)
PRO
$24.90 / month
- Everything in Starter
- Production API keys and webhooks: 2,000 calls a day
- Watched folder and database sources
A signed-in Free user can start a 14-day trial by hand from the dashboard banner or the app’s paywall (no card): it unlocks Excel and CSV binding, bulk barcodes and the production API. It does not start by itself at signup. Yearly billing is ten months for twelve ($79.90 Starter, $249.00 Pro). All plans and limits: pricing.
QUESTIONS / FAQ
Frequently asked questions
How do I start a LabelInn workflow from my own code?
Create an inbound trigger with workflows.create_trigger (signed if you want a secret), then call workflows.fire with the workflow id, the token and your record. Without an SDK, POST the record as JSON to /v1/workflows/{id}/trigger/{token}.
Do I need an API key to fire a trigger?
No. The token in the URL is the credential, so treat it like a password. A signed trigger additionally needs the X-LabelInn-Signature header.
How is the request signed?
HMAC-SHA256 of the exact request body with the trigger’s secret, sent as X-LabelInn-Signature: sha256=<hex>. The SDKs do it for you; from a shell use openssl dgst -sha256 -hmac.
Is a test run the same as firing?
No. workflows.test walks the graph with a sample record and prints nothing. fire is a real run and labels print.
Can I try it before paying?
Test keys and the read-only sandbox are free. Workflows are on Starter and above; the production API is on Pro. A signed-in Free user can start a 14-day trial by hand from the dashboard banner or the app’s paywall (no card): it unlocks Excel and CSV binding, bulk barcodes and the production API. It does not start by itself at signup.
KEEP GOING
Related
NEXT STEP / LABELINN
Let your code start the print logic
Download LabelInn, build the workflow once, trigger it from any system. · Free plan, no card · Signed triggers · Windows and Mac